Physical Penetration Testing for Organisations
Security plans, access controls and organisational procedures only provide effective protection when they work together reliably in day-to-day operations. Physical penetration testing examines that real-world effectiveness under realistic, controlled conditions. 3-core plans and delivers authorised physical security tests for organisations, sensitive sites and operators of critical facilities, showing where protective measures work, where interfaces fail and which improvements can deliver the greatest security benefit.
We do not look at individual doors, fences or technical systems in isolation. The focus is the complete protective-security chain: perimeter security, access and visitor processes, security guarding, employees, detection, reporting routes, escalation and operational response. The result is evidence of how security performs in practice rather than a purely theoretical assessment.
- Realistic test scenarios rather than document review alone
- Clear scope, defined boundaries and agreed Rules of Engagement
- Assessment of technology, processes, people and response as an integrated system
- Documented findings and prioritised, practical improvement actions
What is physical penetration testing?
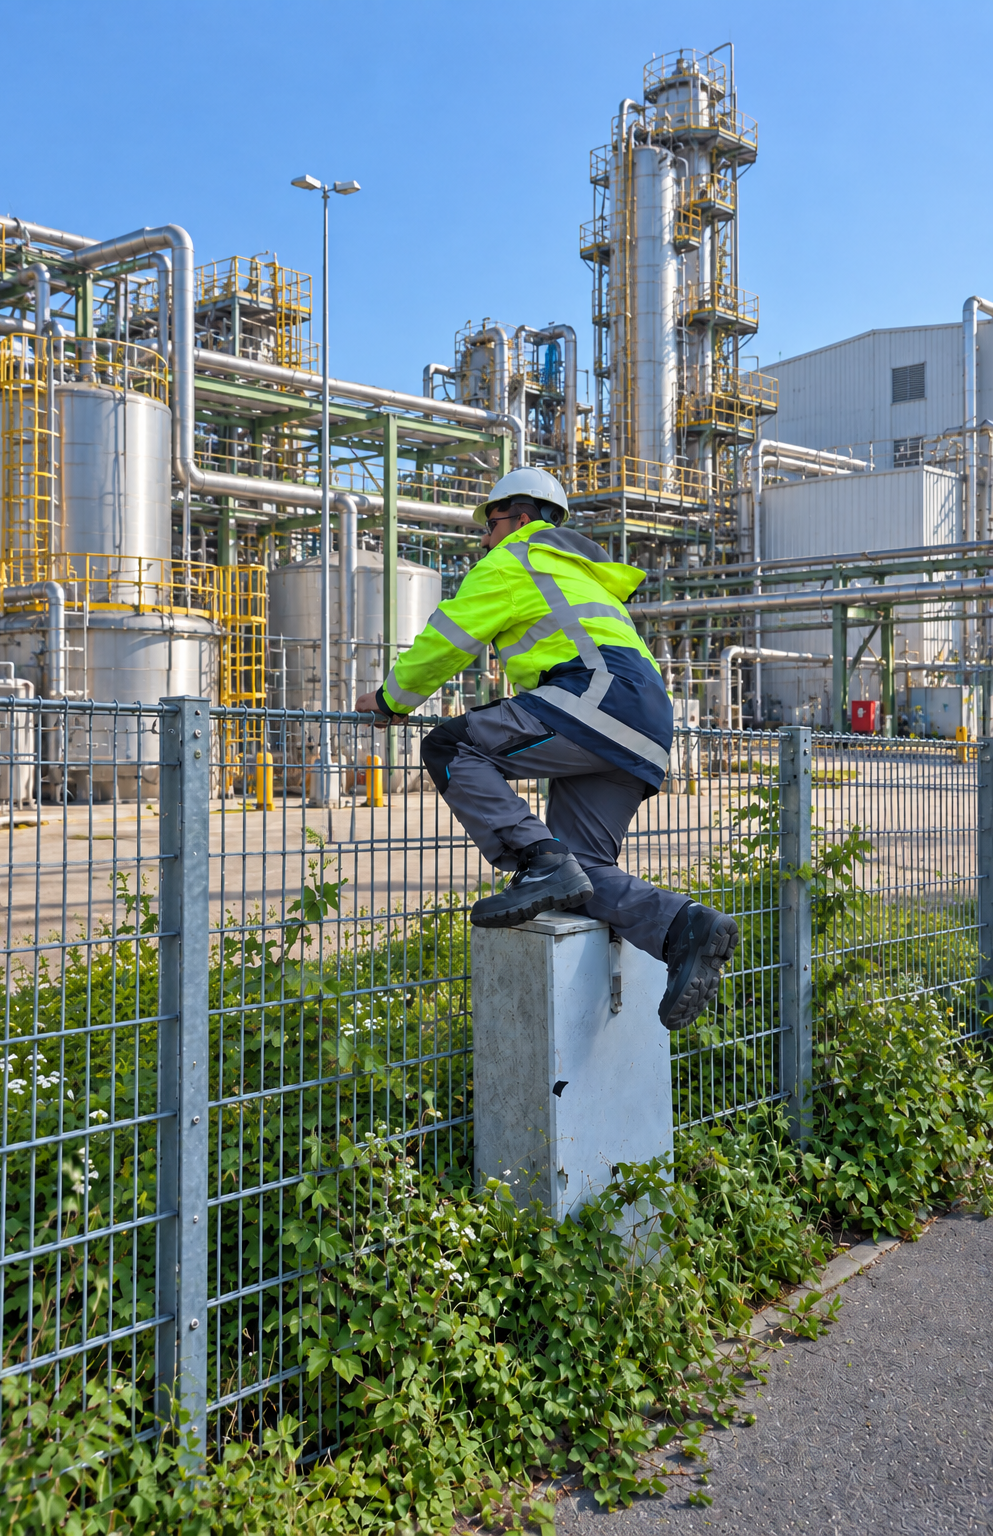
Physical penetration testing is an authorised and controlled security assessment in which agreed test scenarios are used to examine whether existing physical security measures work in practice. Unlike a conventional review, the purpose is not simply to confirm that controls exist. The key question is whether those controls function in real operating conditions and whether unauthorised access or other unwanted activity is detected, prevented or handled appropriately.
Depending on the objective, testing can cover access points, transitions between security zones, visitor and supplier processes, security-officer procedures, employee security awareness, reporting routes and escalation arrangements. Every physical penetration test is limited to a clearly defined scope. Permitted and excluded activities, protected areas, time windows, authorised contacts, stop conditions and escalation procedures are agreed in advance.
The value lies in connecting planning with reality. A Site Security Plan defines how a site should be protected; physical penetration testing shows how well those arrangements perform under controlled real-world conditions. This provides a sound basis for confirming effective measures, prioritising weaknesses and directing future investment more effectively.
Why physical security should be tested in practice, not only on paper
Physical security arrangements often evolve over many years: new access-control systems, changed reception processes, external guarding providers, additional security zones or new supplier and visitor routes. Each measure may be sensible in isolation. Weaknesses, however, often arise where several layers have to work together or where operational routines no longer match the intended process.
Physical penetration testing makes these interfaces visible. A technical access-control system may work correctly while an organisational exception is not controlled consistently. Equally, suspicious activity may be detected without the subsequent reporting or escalation route operating reliably. The assessment therefore considers not only whether a particular control can be challenged, but how the organisation responds as a whole.
Equally important, testing does not only identify deficiencies. It can also evidence measures that successfully detect, delay or stop a test scenario. This creates a balanced assurance picture that security leaders can use when discussing priorities with management, sites and service providers.
Physical penetration testing: what can be assessed?
The test areas depend on the security objectives, site, existing controls and required depth of testing. A physical penetration test must have a clearly agreed scope before delivery begins. Typical areas include:
Perimeter security and site boundaries
We assess relevant external areas, vehicle and pedestrian access points, gates, transitions and defined security boundaries. The question is whether barriers and control points deliver the intended protective effect during normal operations.
Access control and authorisation management
Testing can cover access-control logic, permissions, security zones, doors, controlled entry points and organisational approval processes. Physical penetration testing helps determine whether technical and procedural controls operate consistently together.
Visitors, suppliers and contractors
External visitors and changing contractors are part of normal operations at many sites. We can assess registration, identity verification, escorting, issue and return processes, handover points and the handling of agreed exceptions.
Security guarding and control processes
Security officers play a central role in detection, challenge, verification and escalation. Testing can examine whether responsibilities are clear, the right information is available and agreed procedures are applied consistently in practice.
Employee security awareness
Even strong technical controls depend on security-conscious behaviour. Testing can therefore examine whether unusual activity is noticed, appropriately challenged and reported through the intended routes. The purpose is not to judge individual employees, but to understand the effectiveness of the organisation’s security culture. Where required, findings can feed into targeted Physical Security Awareness Training.
Detection, reporting, escalation and response
A security event is only managed effectively when detection and response work together. Where relevant, we consider reporting routes, escalation, responsibilities, intervention and the coordination between internal teams and external security providers.
When is physical penetration testing appropriate?
Physical penetration testing is particularly useful when protective measures are already in place and their real-world effectiveness needs to be validated. It can focus on a specific question or be designed as a wider assessment across several layers of security.
- after the introduction or significant revision of a Site Security Plan
- after changes to a site, access processes or security zones
- where recurring observations or suspected weaknesses require practical validation
- before major investment in structural or technical security measures
- for independent assurance of existing protective measures
- at sensitive production, energy, logistics, administrative or campus sites
- as a targeted follow-up to a site assessment or Site Security Review
Physical penetration testing is not always the right first step. If the organisation first needs clarity on risks, security requirements or the current state of a site, a structured assessment or the development of a Site Security Plan may be more appropriate. We clarify that distinction during scoping.
From security objectives to validated effectiveness
Physical penetration testing delivers the greatest value when it is treated as part of a structured improvement cycle rather than a one-off event. Our six-step approach moves from clear objectives and authorisation through controlled testing to prioritised improvement and, where useful, re-testing.

1. Define objectives and scope
We first clarify the question the engagement must answer. Together, we define the sites, protected areas, relevant assets, time windows and required depth of testing. Permitted and excluded activities, authorised contacts, stop conditions and safety and escalation arrangements are also agreed. This gives the engagement a clear, authorised and controllable framework.
2. Understand the baseline and plausible test paths
We then review the conditions relevant to the engagement. Depending on scope, this may include selected security documentation, publicly available information and focused on-site observation. The objective is not to redesign the entire security arrangement, but to derive realistic test paths from the site’s actual exposure and operational routines.
3. Develop test scenarios
We develop scenarios from the agreed objectives and baseline. These may relate to access management, visitor and supplier processes, security guarding, security zones or organisational response. Where relevant to effectiveness, the scope can include different operating periods such as day and night operation or shift changes.
4. Conduct controlled testing and observe responses
Testing is conducted only within the agreed Rules of Engagement. Our consultants document relevant observations and responses in a traceable manner. The assessment considers the full protective-security chain: which control detects the scenario, who responds, whether the situation is assessed correctly and whether escalation works as intended.
5. Evaluate and prioritise findings
Following delivery, the relevant observations are evaluated systematically. We distinguish between effective controls, opportunities for improvement and weaknesses. Findings are considered in context and prioritised according to risk, security impact and practicality, creating a decision-ready assessment rather than an unstructured list of issues.
6. Plan improvements and re-test where appropriate
In the findings workshop, we explain the results and agree sensible next steps with the responsible teams. Depending on the outcome, this may involve process changes, clearer responsibilities, training or technical and physical improvements. A focused re-test can then validate whether material improvements have achieved the intended effect.
What do you receive after the test?
Physical penetration testing should support real decisions. We therefore present the results so that both operational security teams and management can understand which controls work, where action is required and which improvements should be prioritised.
- a documented test record and traceable findings
- an assessment of relevant weaknesses and effective controls
- analysis of root causes, interfaces and potential security impact
- prioritised recommendations, including practical quick wins and structural improvements
- a management-ready final report
- a findings workshop with the relevant stakeholders
- optional support with improvement planning and implementation
- optional focused re-testing after material improvements have been implemented
The exact deliverables are agreed during scoping, so it is clear from the outset which questions the engagement will answer and what decision-making basis you will receive.
Physical penetration testing: our services at a glance
3-core structures each engagement modularly. Testing can therefore be tailored to a single site, a particular control or a more complex security organisation. Typical service components include:
- Scoping, objective definition and Rules of Engagement
- Review of relevant security information and operational processes
- Open-source information review (OSINT) and site-specific information analysis
- Focused on-site observation of operational routines and interfaces
- Development of realistic test paths and scenarios
- Controlled physical security testing within the authorised scope
- Observation of access, control, reporting, escalation and response processes
- Structured documentation and evaluation of findings
- Prioritisation of improvements by risk, security impact and practicality
- Management-ready reporting and presentation of results
- Support with the further development of the Site Security Plan and related measures
- Focused re-testing to validate implemented improvements
Every engagement is tailored to the specific objective. Scope and intensity are driven by the required level of protection, site structure and the questions that matter to your organisation rather than by a fixed testing package.
Physical penetration testing, Security Assessment or Site Security Plan?
These services answer different questions and should remain clearly separated. This helps organisations select the right format and keeps each 3-core service page focused on a distinct search and buyer intent.

Three examples from physical security assurance
The following case studies show how 3-core has applied practical physical security testing and site assessments in different situations. They are kept deliberately concise on this service page; the full project pages provide the supporting detail.
Physical penetration test at a campus site
Security check for a public institution
Site Security Reviews
Why 3-core for physical penetration testing?
3-core combines practical security testing with experience in Security Management, risk assessment and the development of Site Security Plans. This means we do not treat findings in isolation; we assess what they mean for the wider security organisation, especially where technical, organisational and personnel controls depend on one another.
- Independent consultancy with a clear separation between assessment and product sales
- Experience with sensitive sites and critical infrastructure environments
- Structured scoping, written authorisation and controlled delivery
- Integrated view of technology, processes, security guarding and employees
- Management-ready reporting rather than a simple list of findings
- Prioritised improvements based on risk, impact and practicality
- Clear connection to existing Site Security Plans and site-security improvement programmes
Our aim is that physical penetration testing does not end with a binary conclusion that something “worked” or “failed”. The important question is why the protective-security chain performed as intended, where it broke down and how the organisation can improve security pragmatically. The broader governance and improvement framework is covered on our Security Management pillar page.
Would you like to test your physical security under realistic conditions?
Physical penetration testing provides evidence of how resilient your protective measures are in day-to-day operations. Together, we define the relevant security objectives, a controlled scope and realistic test scenarios. You then receive traceable findings and practical recommendations for strengthening physical security.
Tell us which sites, processes or protective measures you want to validate. In the initial discussion, we clarify whether physical penetration testing is the right format for your question and what level of testing is appropriate.
Physical penetration testing: frequently asked questions
Physical penetration testing is an authorised and controlled assessment of physical security measures under realistic conditions. Pre-agreed scenarios are used to determine whether protective measures, processes and response arrangements work in practice as intended.
A Security Assessment records and evaluates the current security position in a structured way. A physical penetration test goes a step further by practically challenging selected controls through agreed scenarios. The two formats can complement each other.
Depending on scope, testing can cover perimeter security, access management, security zones, visitor and supplier processes, security guarding, employee security awareness, reporting routes and organisational response. The exact scope is agreed with the client before testing begins.
Objectives, permitted methods, boundaries, authorised contacts, stop conditions, safety arrangements and escalation routes are agreed in advance. Testing takes place only within that authorised framework, allowing the exercise to remain realistic while staying controlled.
That depends on the objective. We agree with the client which people need to be informed. For some assurance questions, a limited need-to-know group can be appropriate so that normal processes can be observed with minimal distortion.
The effort depends on factors such as the number and size of sites, the scope, the planned scenarios and the relevant operating periods. Following scoping, 3-core can define a proportionate project structure and level of effort.
The final report documents relevant observations, evaluates findings and sets out prioritised recommendations. It can also record effective controls and positive responses so that the organisation receives a balanced picture of actual performance.
Yes. Depending on the findings, 3-core can support changes to processes, responsibilities and the Site Security Plan as well as the prioritisation of further improvements. A subsequent re-test can validate whether material changes have achieved the intended effect.
Physical penetration testing does not need to follow a universal interval. Useful triggers include material changes to the site, access organisation or Site Security Plan, as well as the implementation of major improvement measures. Frequency and scope should be risk-based and linked to the specific assurance question.